Keeper Security · Articles
Finding Out Your Password Was Stolen Before It's Used Against You
Finding Out Your Password Was Stolen Before It's Used Against You
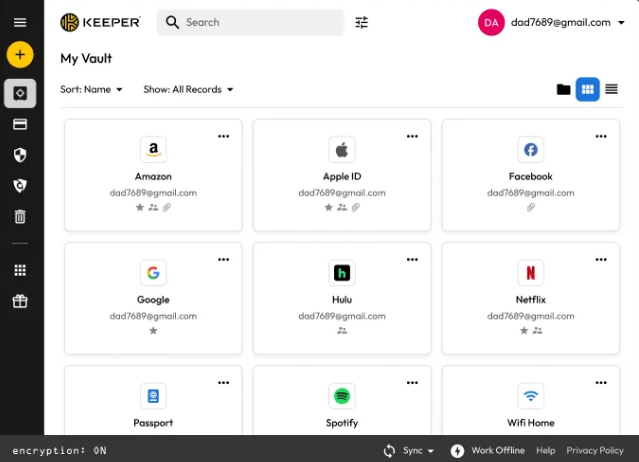
A password breach often goes unnoticed for months — the first sign is usually unauthorized account activity, by which point real damage may already be done. Keeper's BreachWatch is specifically built to close that gap, continuously checking stored credentials against breach data rather than waiting for a problem to surface.
A genuinely different approach than most monitoring services
Most dark web monitoring services work by sending your email address or a hashed password to a third-party service for matching — meaning your data leaves that service's security boundary entirely. BreachWatch is specifically built to work differently, preserving Keeper's zero-knowledge architecture throughout the entire monitoring process.
An anonymized hash, not raw credential data
When BreachWatch activates, the client computes an HMAC_SHA512 hash of each stored password and sends only that anonymized hash to Keeper's servers — meaning Keeper itself never sees the actual password being checked.
A database spanning over a billion records
BreachWatch checks against a database of more than a billion breach records — described as the most in-depth monitoring publicly available, rather than a smaller, less comprehensive breach list that might miss genuine exposure.
Immediate, actionable alerts, not just notification
When BreachWatch detects a breached credential, it sends an automatic notification allowing immediate action — and when the password is updated through Keeper, the new credential is automatically saved under the same record, keeping the whole remediation process within one workflow.
A patented security architecture
BreachWatch is specifically built on a patented method for dark web analysis, ensuring no one — including Keeper itself — knows which specific websites a user has accounts with, or whether those passwords have actually been breached, beyond the anonymized match itself.
Genuine enterprise oversight without compromising individual privacy
For business use, Keeper administrators can see which users have exposed credentials without ever having direct access to those users' actual passwords — a meaningful balance between organizational security oversight and individual employee privacy.
Integration with existing security infrastructure
BreachWatch events can feed into SIEM platforms and convert into tickets within systems like Jira and ServiceNow through Keeper's Advanced Reporting and Alerts Module — letting breach detection plug directly into an organization's existing incident response workflow rather than existing as an isolated alert system.
Available across every Keeper tier
BreachWatch is available as an add-on across Keeper Personal, Family, Business, and Enterprise plans — letting the same dark web monitoring capability scale from individual use through to full organizational deployment.
At a glance
Product: ** BreachWatch by Keeper Security
Type: ** Dark web monitoring add-on
Database: ** 1+ billion breach records
Security: ** Zero-knowledge, HMAC_SHA512 hashing
Platforms: ** Web, desktop, iOS, Android
Available for: ** Personal, Family, Business, Enterprise plans
Who it suits
BreachWatch suits anyone already using Keeper Password Manager who wants continuous, proactive monitoring for exposed credentials, rather than discovering a breach only after an account has already been compromised. Anyone not yet using a password manager should start with Keeper's core Password Manager first, since BreachWatch functions specifically as an add-on layer on top of that existing vault. Explore Keeper Security's BreachWatch — **
Visit store